Mobile application Penetration Testing
Master Android application penetration testing from scratch. Start with the fundamentals (Android architecture, sandbox, permissions model), then dive deep into static and dynamic analysis. Learn to decompile APKs, read Smali code, reverse engineer app logic, intercept traffic, and manipulate apps at runtime. Get hands-on with every major tool: MobSF, Frida, Medusa, and Drozer, plus native hooking and Smali patching. A practical course aligned with OWASP Mobile Top 10 and eMAPT preparation.
This course takes you through mobile application penetration testing from the ground up, covering both Android and iOS platforms. You will start with environment setup and APK/IPA structure, then move into static analysis: decompiling, reverse engineering, hardcoded secrets, insecure storage, and manifest misconfigurations. From there, you will shift to dynamic analysis, intercepting traffic with Burp Suite, bypassing SSL pinning using multiple techniques, and analyzing runtime behavior. The course then dives deep into hooking and instrumentation: you will learn how to use Frida for JavaScript-based hooking, Objection for rapid automated assessments, and Medusa for modular hook injection. We also cover native hooking (hooking into native libraries and JNI calls), root/jailbreak detection bypass, biometric bypass, and token manipulation. By the end, you will be able to perform a full mobile penetration test, from recon to exploitation to reporting.
Topics covered:
- APK/IPA structure and reverse engineering
- Static analysis (jadx, apktool, MobSF)
- Dynamic analysis and traffic interception
- SSL pinning bypass (multiple methods)
- Frida scripting and hooking (Java and Native layers)
- Objection runtime exploration
- Medusa modular hooking framework
- Native hooks and JNI interception
- Root/Jailbreak detection bypass
- Insecure data storage and token analysis
- Reporting and documentation
Curriculum
Student Feedback
5 based on 2 reviewsLatest Reviews
Hazem ElNaggar
2026-10-08 06:45:19Excellent course with clear explanations and practical hands-on labs that provided valuable real-world skills in Mobile Penetration Testing. Highly recommended!
Jana Ahmed
2026-10-08 09:07:43Good, all of techniques of Static analysis
Lifetime access to all course content
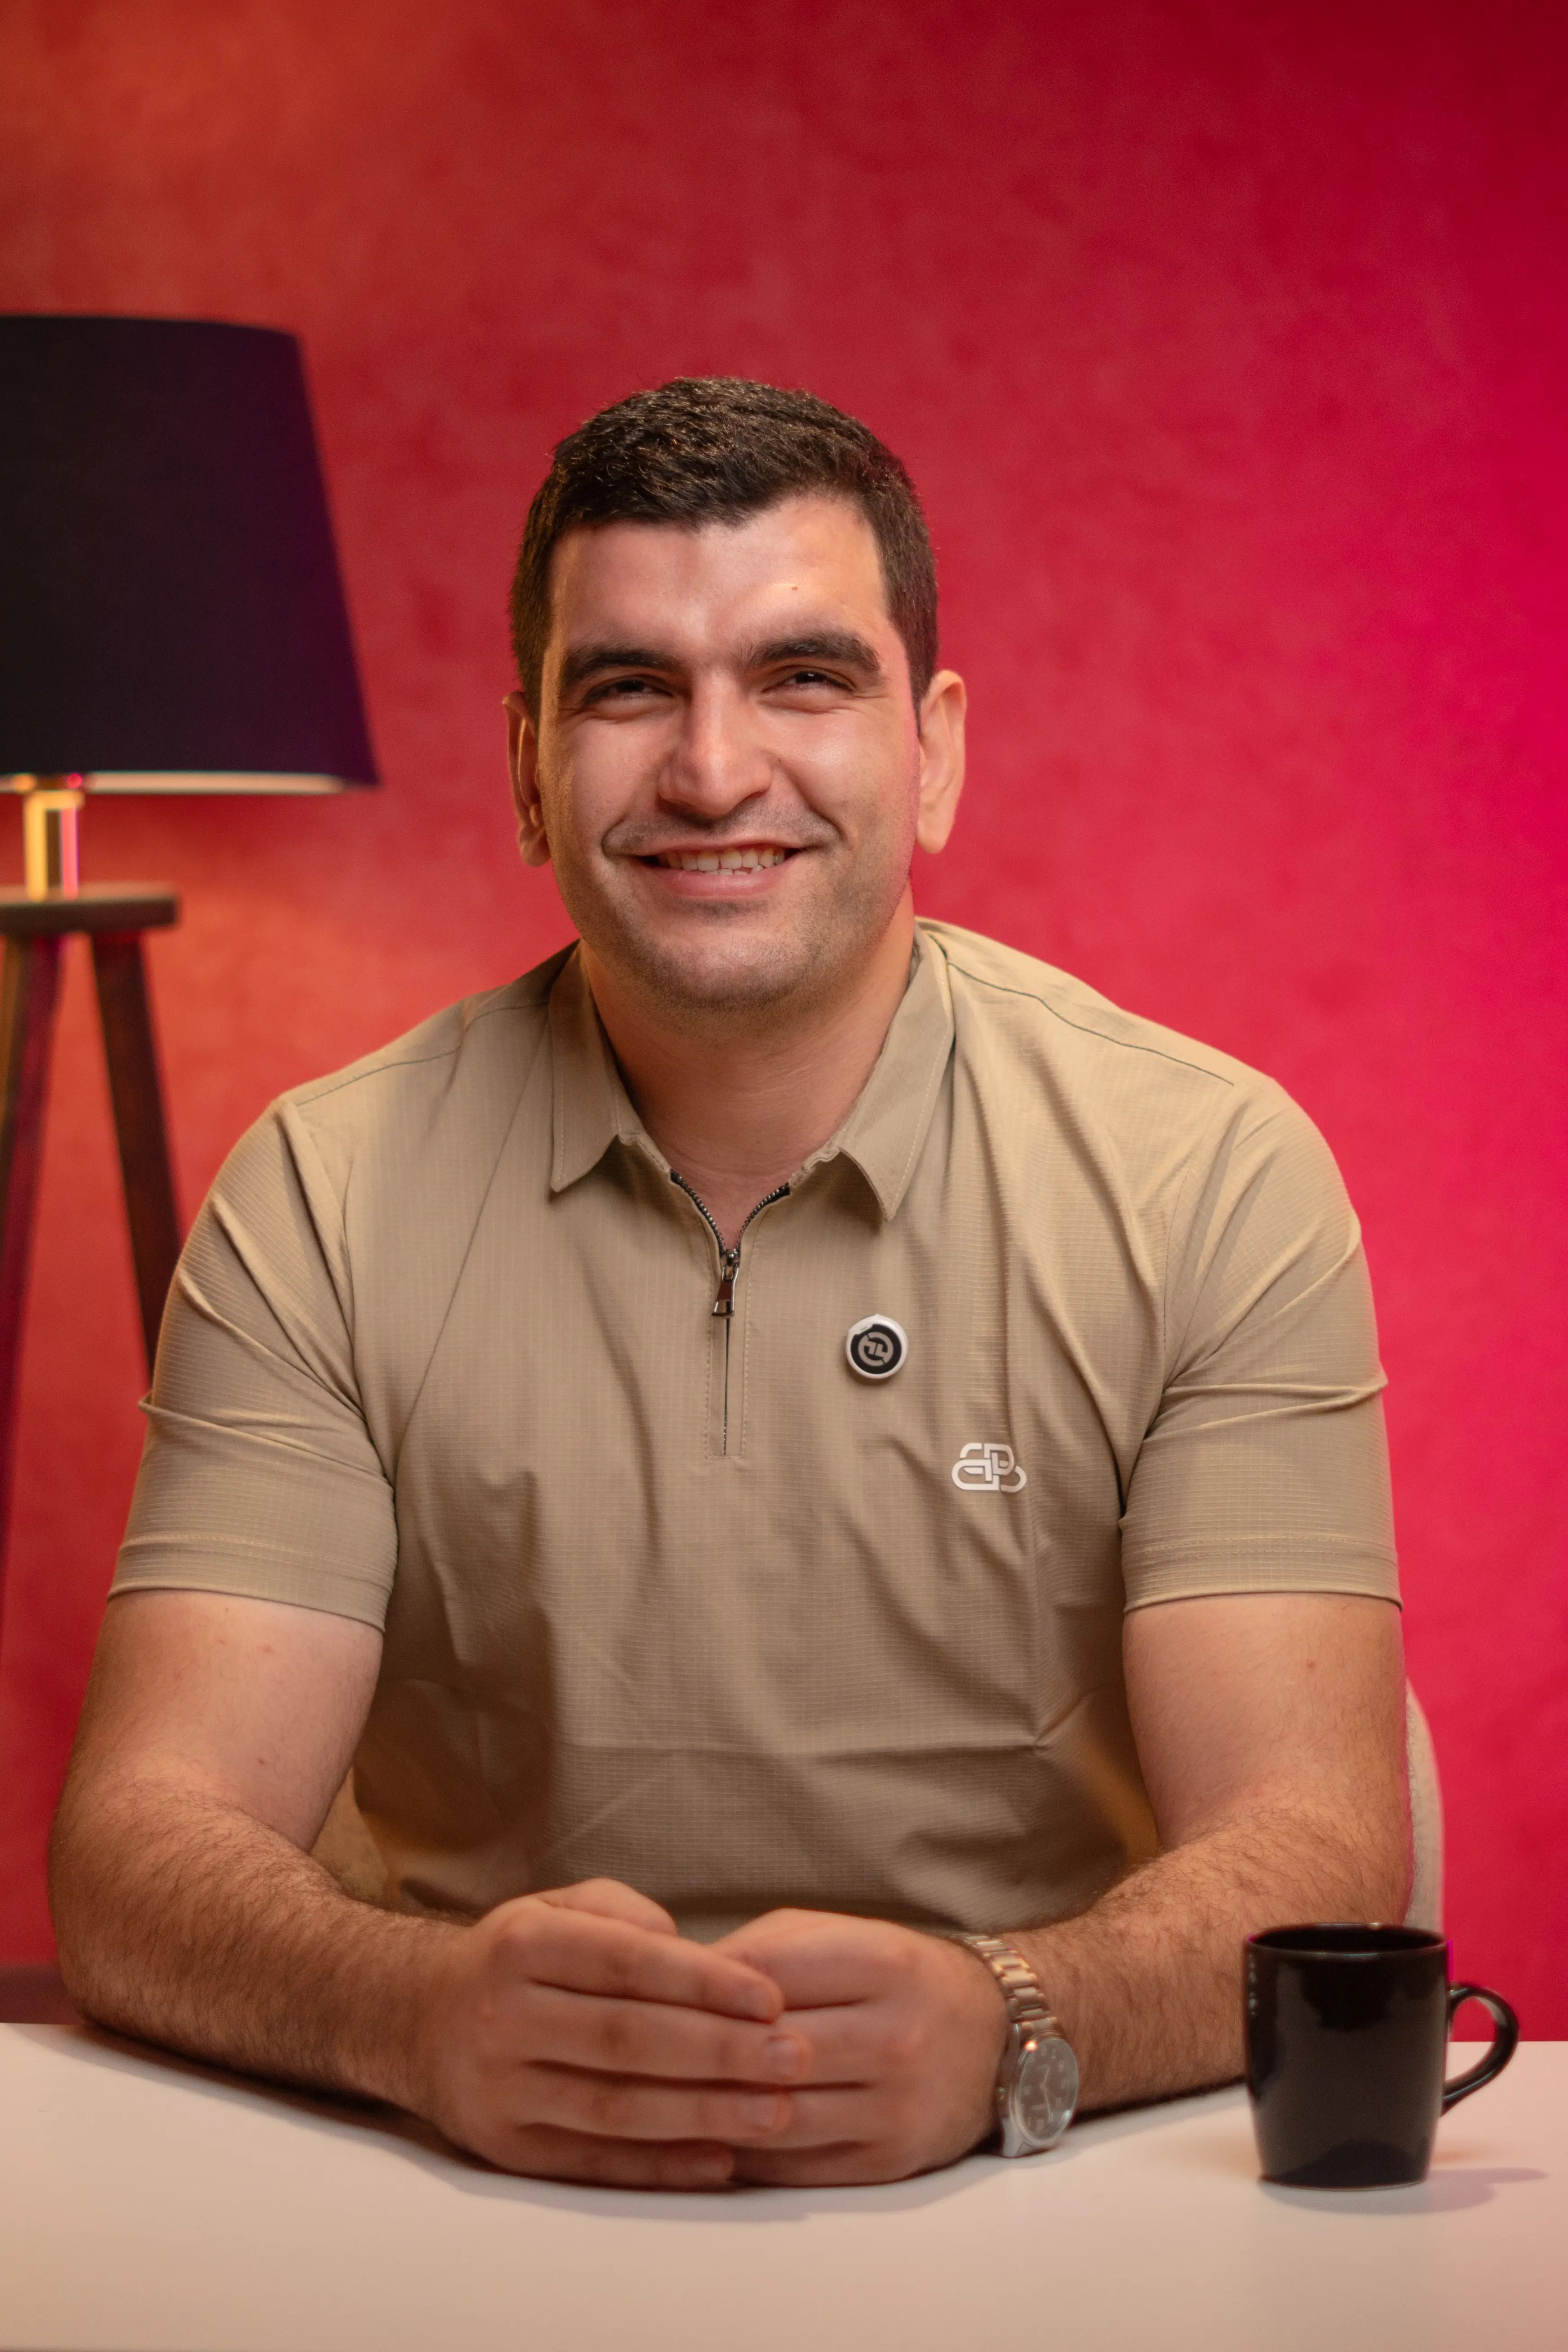
Hossam Shady is the founder of Red Nexus, an expert in cybersecurity and penetration testing.
His passion for the field and real-world experience led him to establish the academy to provide high-quality Arabic content and simplify entering the cybersecurity job market. He focuses on direct, practical training that bridges the gap between learning and applying skills in real scenarios.